What Airgate does
Everything on this page works today. Work in progress is on the roadmap, and every area links to its documentation.
Authentication · Directories · Access policy · Device trust · Certificates · Guest access · Personal devices (BYOD) · Visibility · Switch and router logins · Operations
Authentication
Documentation- 802.1X on wired and wireless with EAP-TLS, PEAP-MSCHAPv2 and EAP-TTLS
- MAC authentication (MAB) for devices that cannot do 802.1X
- PAP, CHAP and MS-CHAP for VPNs and older equipment
- Machine authentication, with a cache so a user sign-in can follow a machine sign-in
- RADIUS and RadSec; Message-Authenticator required on every request (Blast-RADIUS hardening)
- PEAP against on-prem Active Directory through a domain-joined appliance or a site connector
Directories
Documentation- Microsoft Entra ID through Microsoft Graph, with groups and user attributes
- Active Directory and LDAP, Okta and Google Workspace
- SQL databases, REST services, external RADIUS servers and token servers
- Local users with CSV import, and static MAC lists
- Several directories per policy, checked in order; authorisation attributes cached per source
Access policy
Documentation- Policies per network or connection type, each a list of rules; the first match wins
- Conditions on groups, device type and status, MAC lists, Wi-Fi network, switch groups, sign-in method, BYOD enrolment and guest portal sign-in
- Device conditions from Intune, Jamf, SentinelOne and CrowdStrike
- Results as VLAN, role, ACL / Filter-Id, session timeout or vendor attributes
- Change of Authorization and disconnect, from the console or automatically
- Test access: simulate a sign-in and see which rule would match
Device trust
Documentation- Microsoft Intune: managed and compliance state, scheduled and on-demand sync
- Jamf Pro: managed and compliance state for Apple devices
- SentinelOne: agent present and active threats
- CrowdStrike Falcon: sensor present, network containment, Zero Trust Assessment score
- Devices matched by the Intune device ID in their certificate, so private Wi-Fi addresses still match
- Palo Alto Networks User-ID, Fortinet and Check Point identity updates on sign-in
Certificates
Documentation- A certificate authority per tenant, or your own root CA
- SCEP for Microsoft Intune, with each request validated by Intune
- Step-by-step profiles for Windows, macOS, iOS / iPadOS and Android
- OCSP and CRL; a revoked device is disconnected
- Server certificates for RADIUS and the console; trusted external CAs
Guest access
Documentation- Guest portals with self-registration, guest sign-in or accept-terms, in your branding
- Guest Wi-Fi passwords delivered in Microsoft Teams to the employee the visitor picked
- Wi-Fi passes with QR codes from reception, and printable vouchers
- Guest accounts one by one, in batches or from CSV, with expiry
- Receipts by e-mail and SMS
- Access that ends when the guest’s time is up
Personal devices (BYOD)
Documentation- A self-service portal where employees sign in with Entra ID
- AirEnroll apps for Android and Windows; profiles for iPhone, iPad and Mac
- One certificate per device, a device limit per user
- Users see and remove their own devices; administrators can revoke any
Visibility
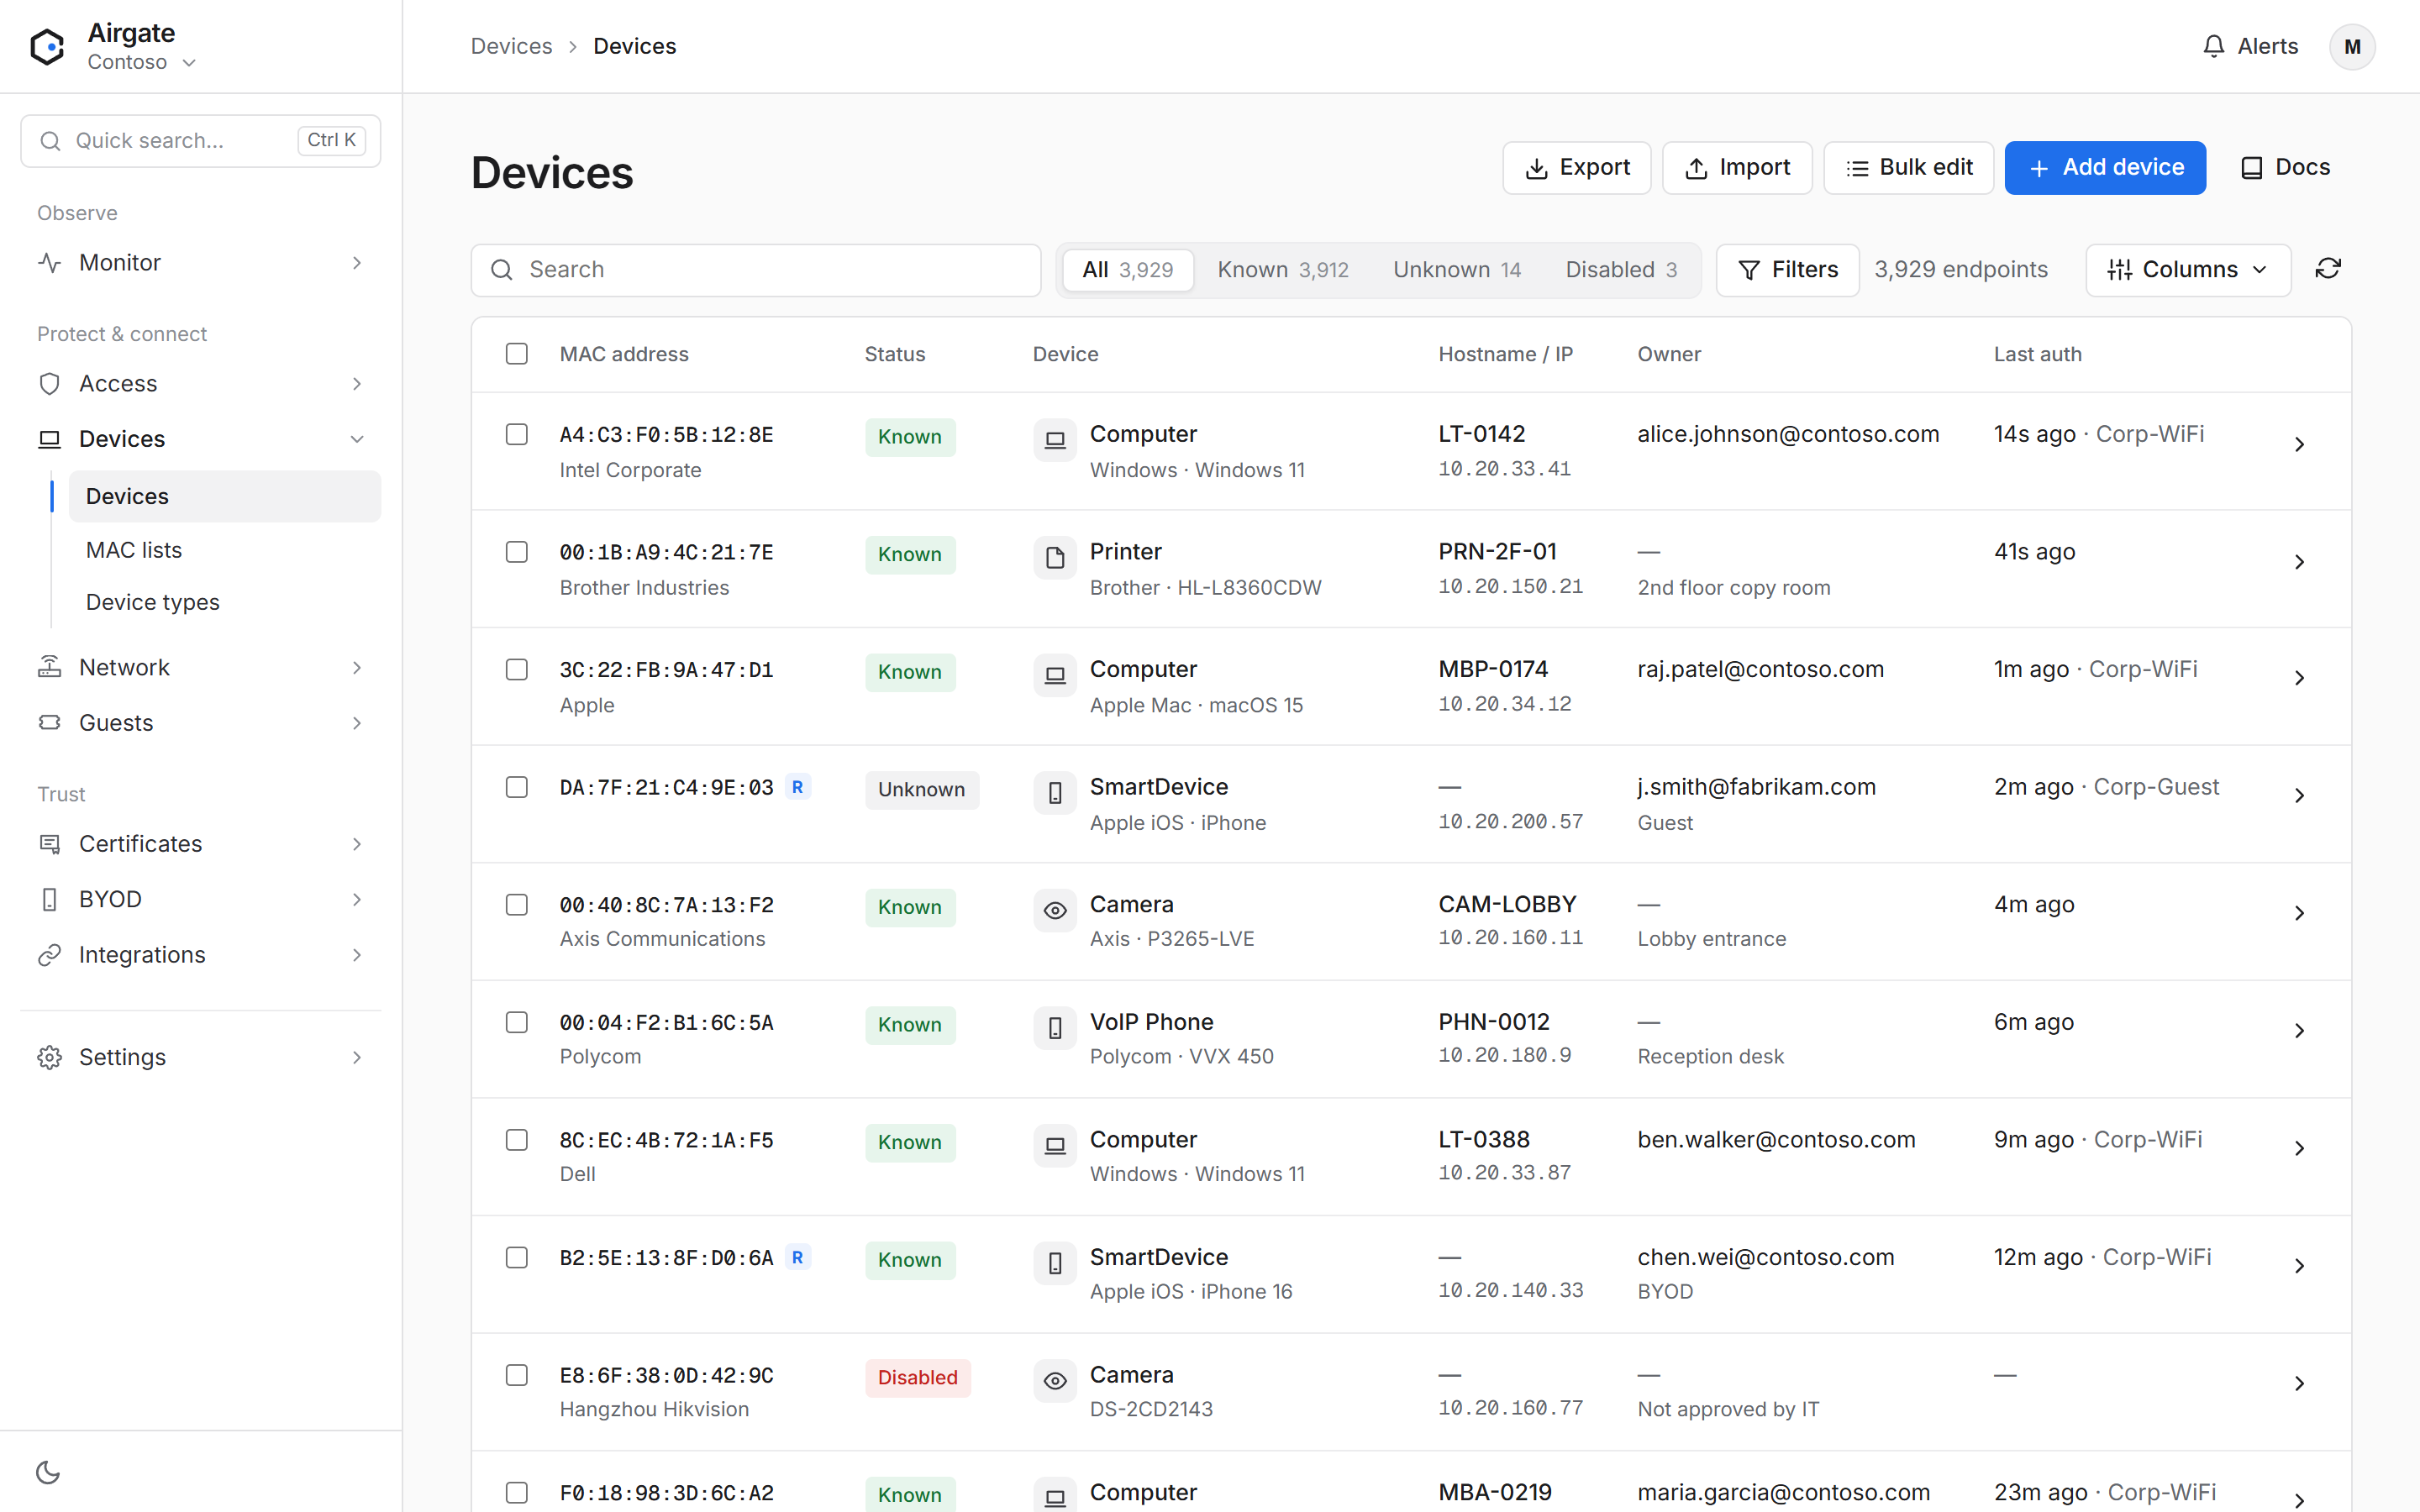
Documentation- Every endpoint on wired and wireless, with type, status and history
- Profiling from DHCP fingerprints, MAC vendor, User-Agent and SNMP
- Private (randomised) MAC addresses flagged
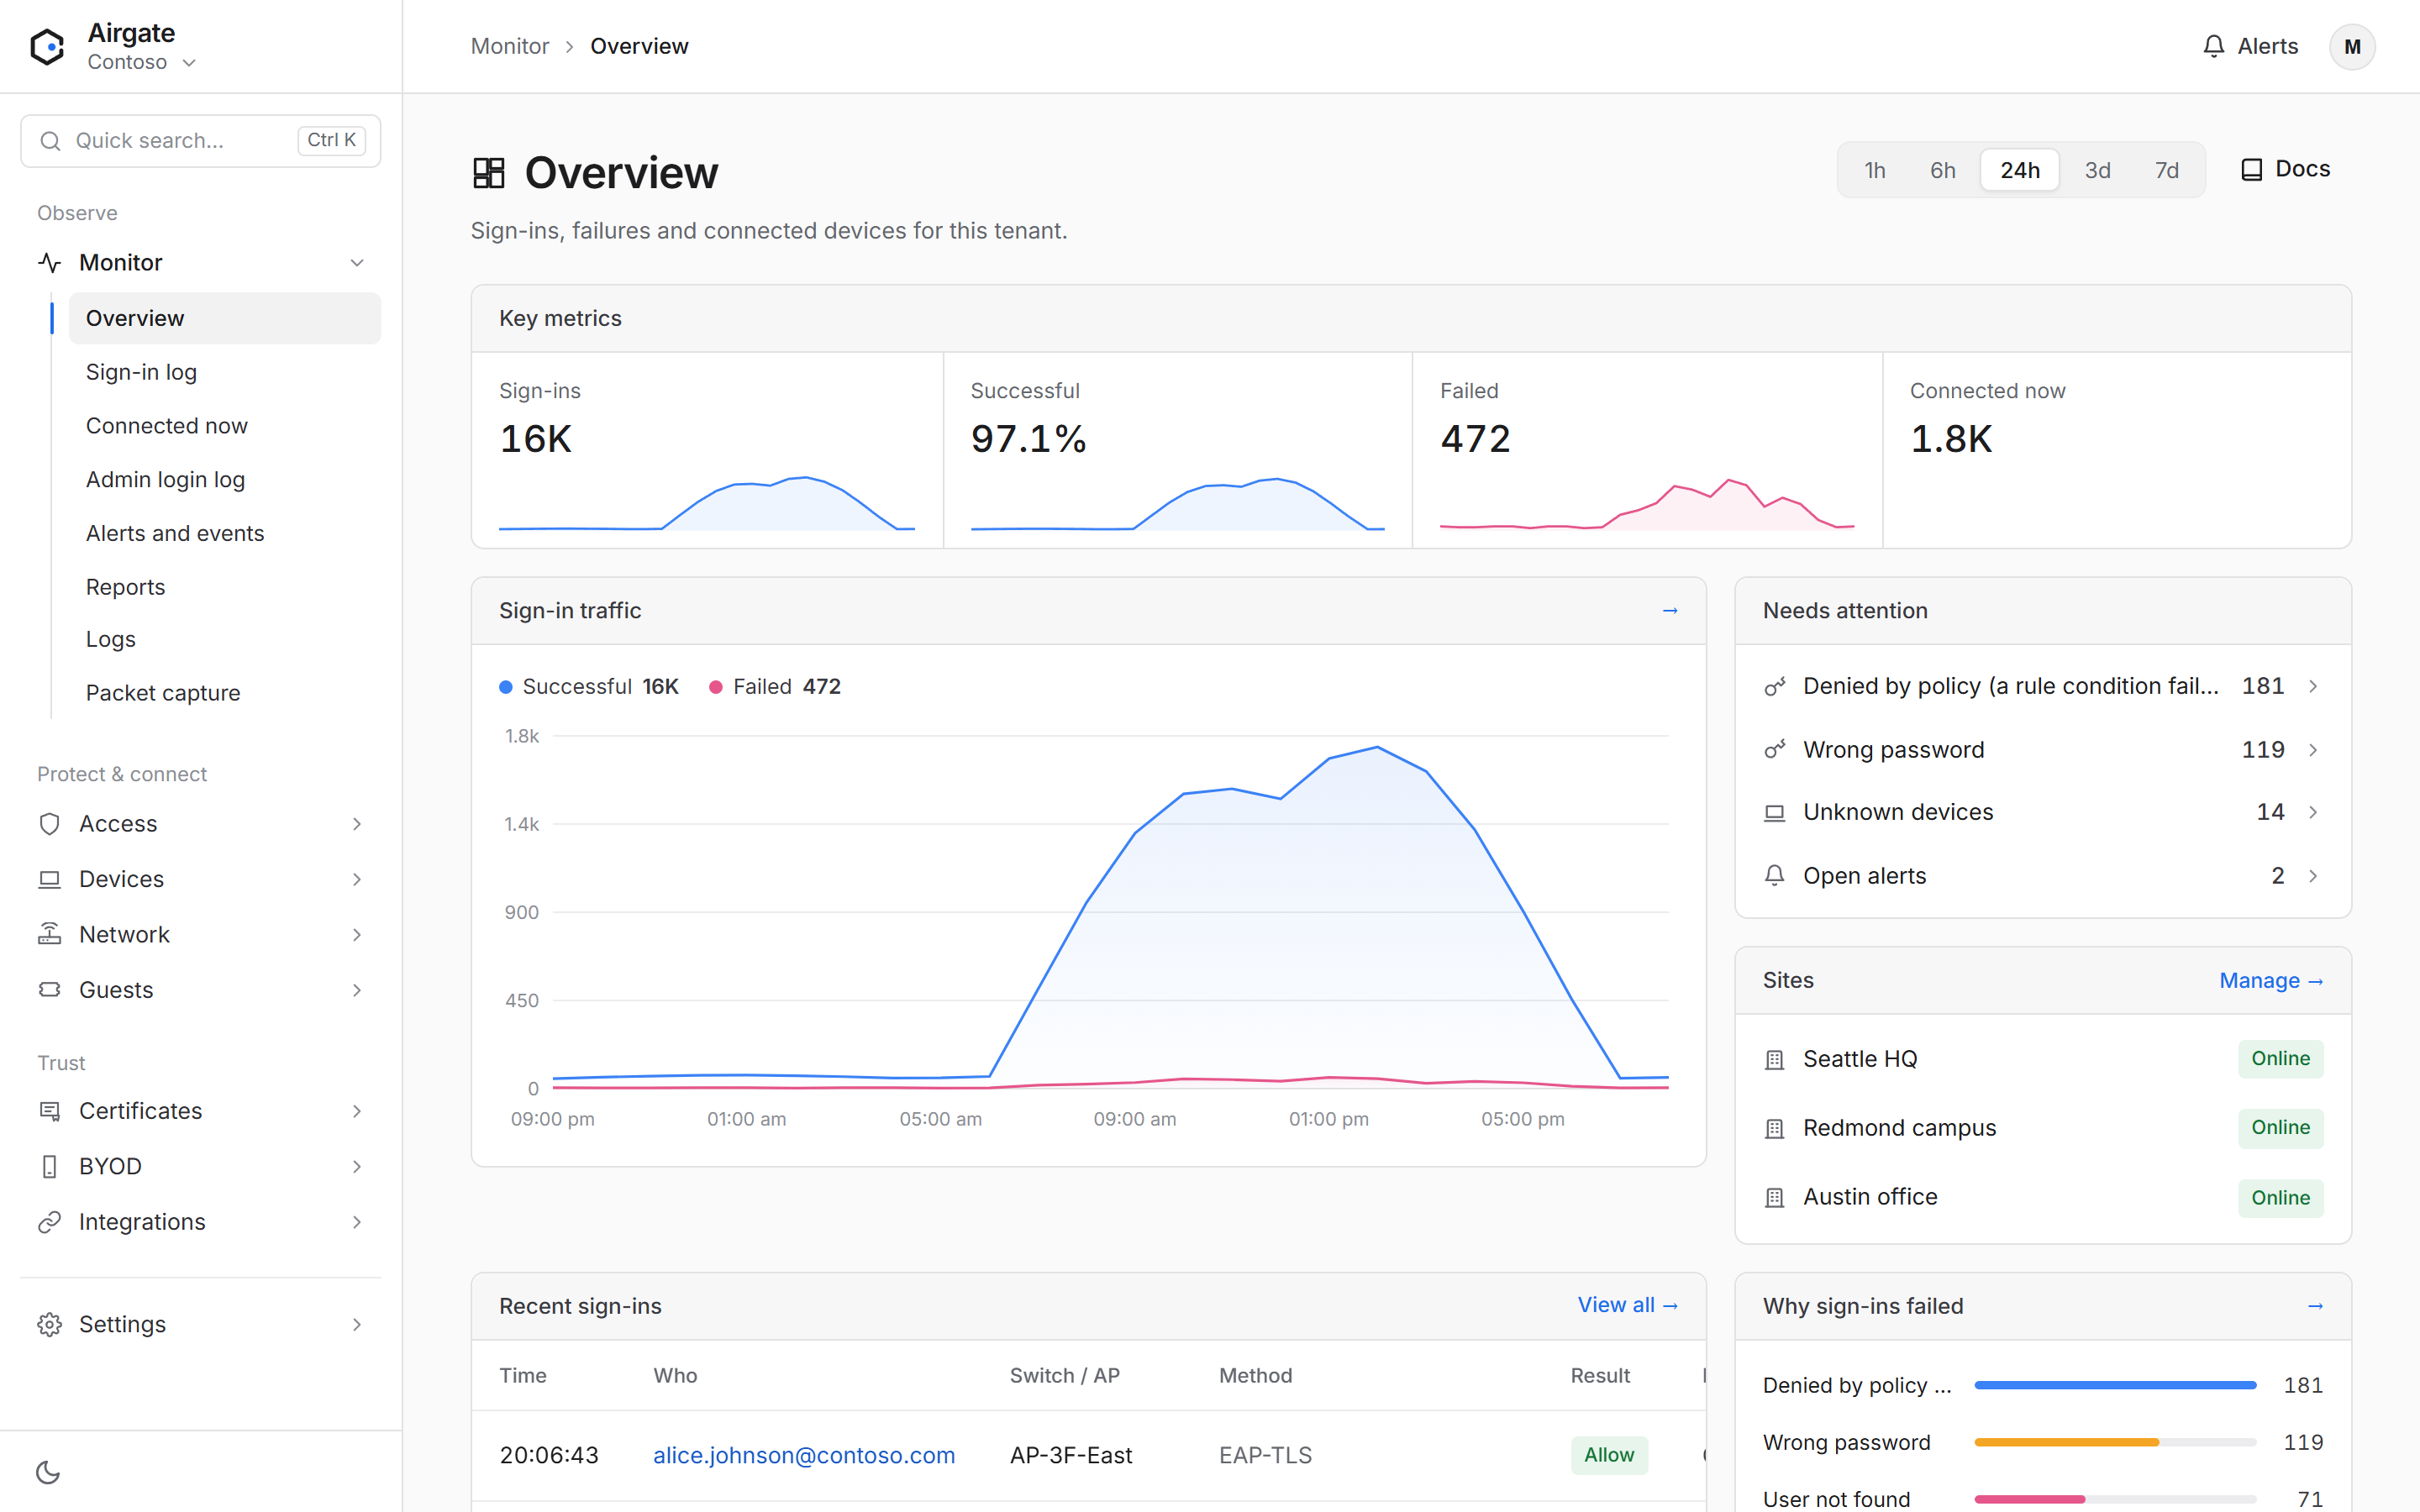
- Live sessions with accounting data; reports and alerts
Switch and router logins
Documentation- TACACS+ with directory accounts and privilege levels
- Command authorisation
- A log of every administrator login
Operations
Documentation- Sign-in log with plain-language diagnosis and the full policy trace
- Debug logging per tenant that switches itself off, and packet capture
- Audit log of every change; syslog, CEF and LEEF export; webhooks
- REST API with API keys; Prometheus metrics
- Tenants and administrator roles; console single sign-on
- Backups and in-place software updates on the appliance